SIS+ Managed OT cyber security
in one service
Regular response rehearsals, continuous OT monitoring and on-call specialist support help you respond faster and reduce the risk of an extended outage.
SIS+ is a managed OT cyber security service for critical infrastructure owners
and operators. It brings together regular response rehearsals, continuous OT monitoring and on-call support when a cyber incident threatens plant operations.
One service. One specialist OT cyber security team. Ready when you need us.
- If controller logic changes outside an approved change, would you know?
- When did your team last practise responding to a cyber incident at your site?
- If a cyber incident happens on the night shift, who responds?
Nobody knows your operation better than the people who run it.
SIS+ adds the visibility and support needed to see what has changed, understand what is reachable and respond when something goes wrong.
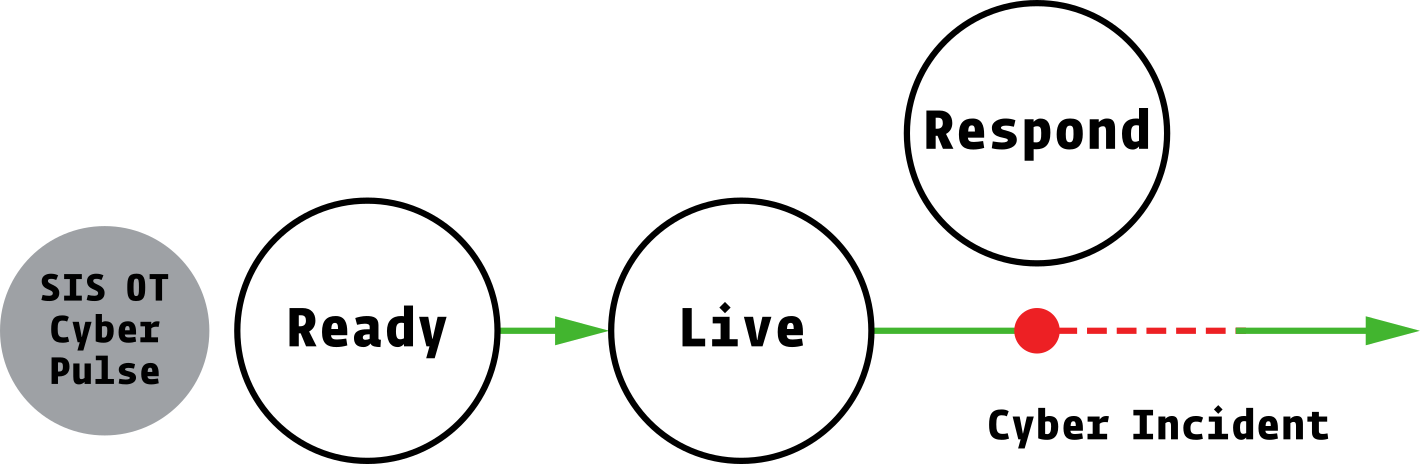
3 connected services, delivered as one: we rehearse with you, we monitor your OT environment, and we respond when a cyber incident occurs.
| Ready | Regular response rehearsals built around your site, clear response procedures and an after-action report after each exercise. |
|---|---|
| Live | Continuous passive OT monitoring that shows what is connected and reachable, and identifies unexpected changes or activity outside normal operating conditions. |
| Respond | On-call OT cyber specialists who help you investigate, contain and recover safely when an incident threatens operations. |
SIS+ brings all three services together.
The scope is based on your number of sites, asset volume and the level of response support required.
Diagram 1: How the service runs
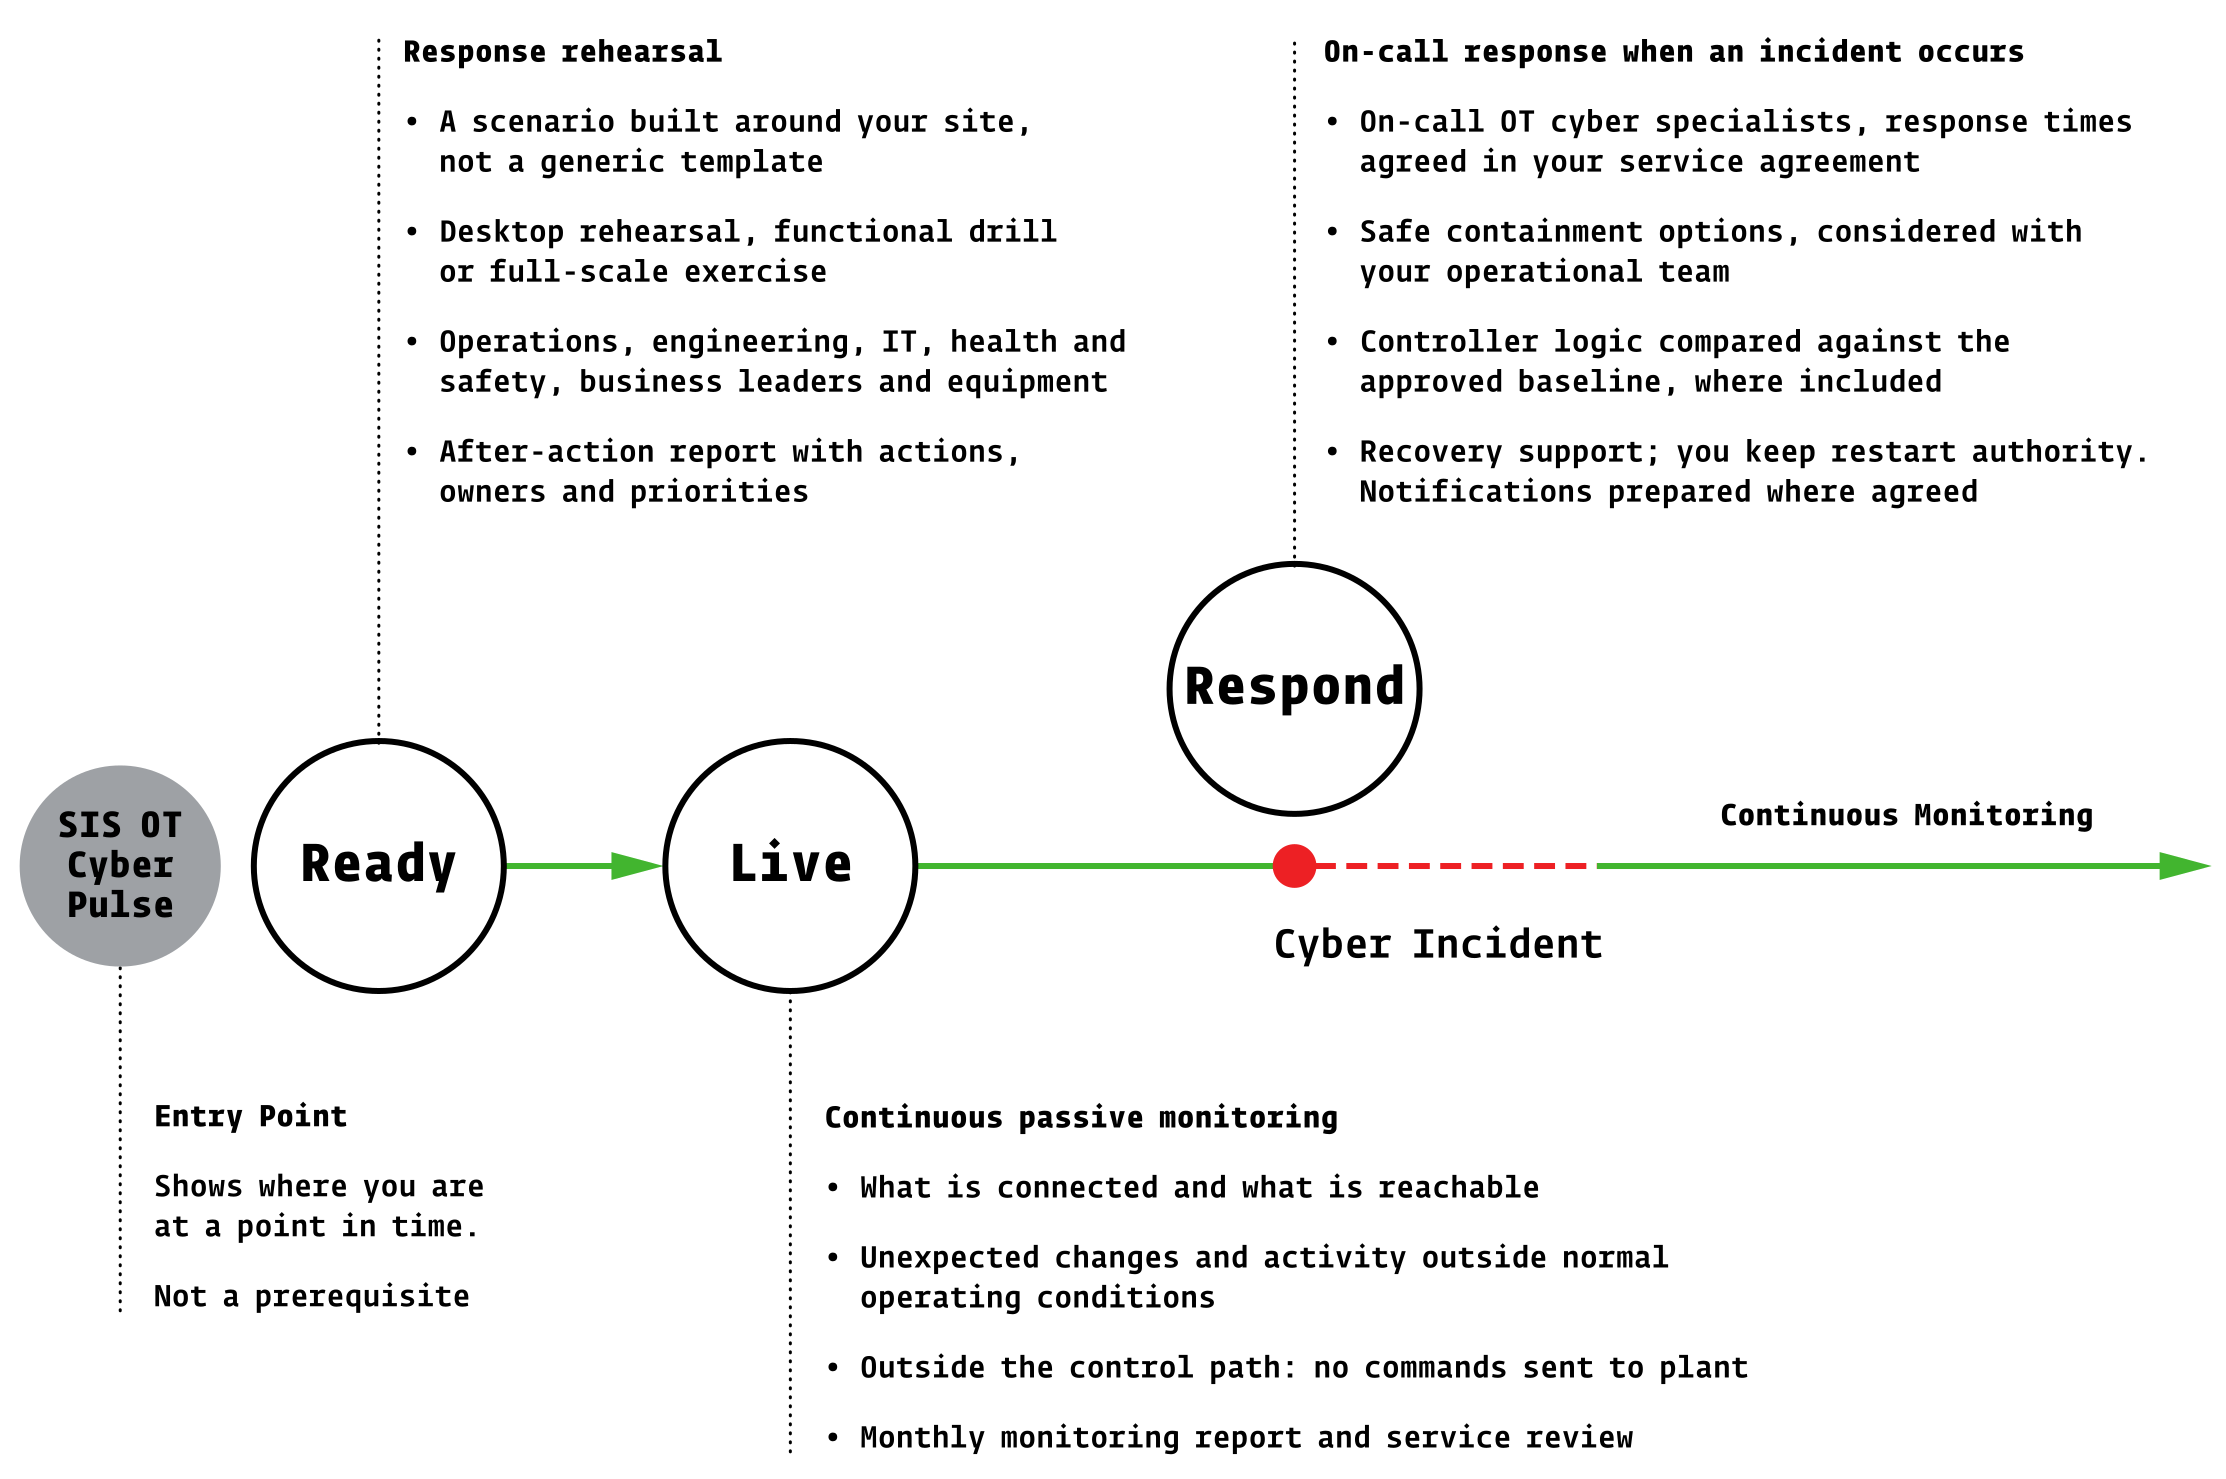
SIS+ service coverage.
Three connected services, delivered as one.
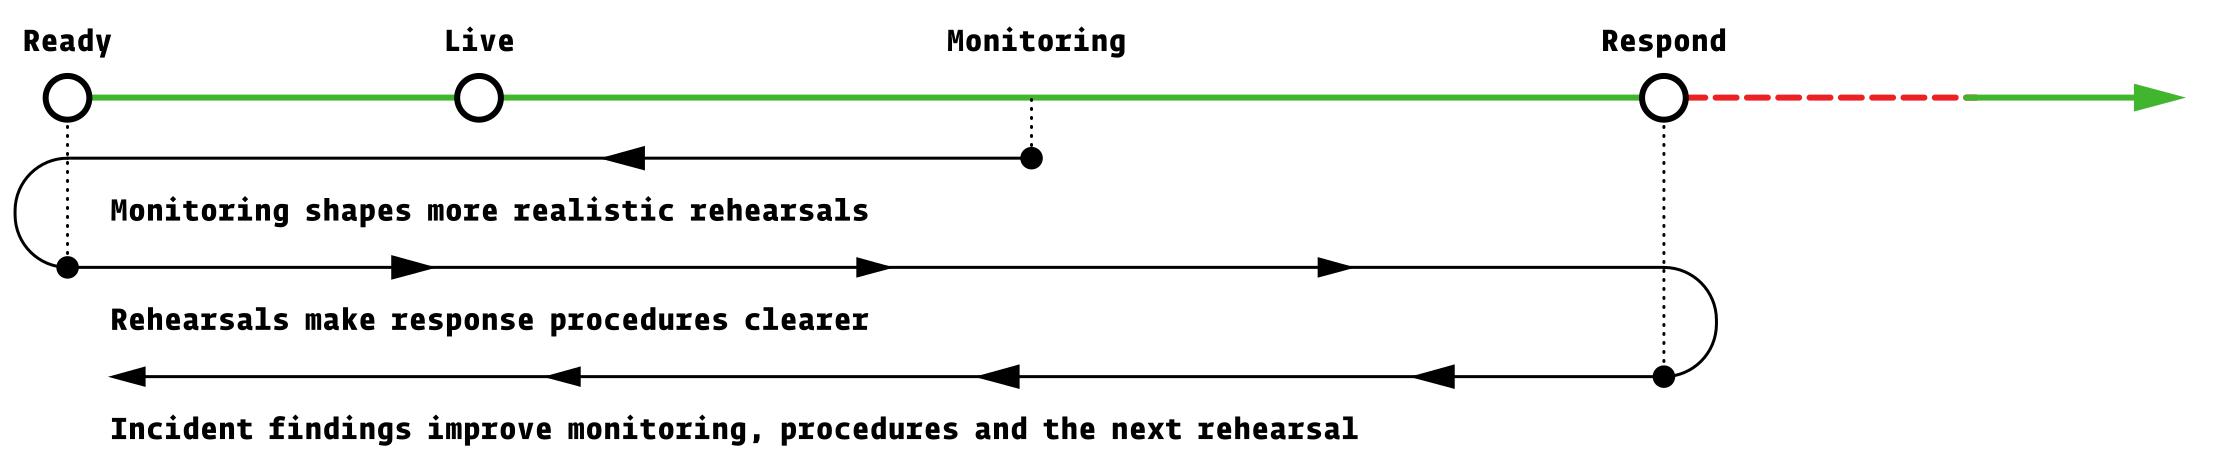
What one learns helps strengthen the other two.
Diagram 2: How each service strengthens the others
SIS+ brings all three services together.
The scope is based on your number of sites, asset volume and the level of response support required.
Diagram 1: How the service runs
Entry Point
Shows where you are at a point in time.
Not a prerequisite
Response rehearsal
- A scenario built around your site, not a generic template
- Desktop rehearsal, functional drill or full-scale exercise
- Operations, engineering, IT, health and safety, business leaders and equipment
- After-action report with actions, owners and priorities
Continuous passive monitoring
- What is connected and what is reachable
- Unexpected changes and activity outside normal operating conditions
- Outside the control path: no commands sent to plant
- Monthly monitoring report and service review
- On-call response when an incident occurs
- On-call OT cyber specialists, response times agreed in your service agreement
- Safe containment options, considered with your operational team
- Controller logic compared against the approved baseline, where included
- Recovery support; you keep restart authority. Notifications prepared where agreed
SIS+ service coverage.
Three connected services, delivered as one.
What one learns helps strengthen the other two.
Diagram 2: How each service strengthens the others
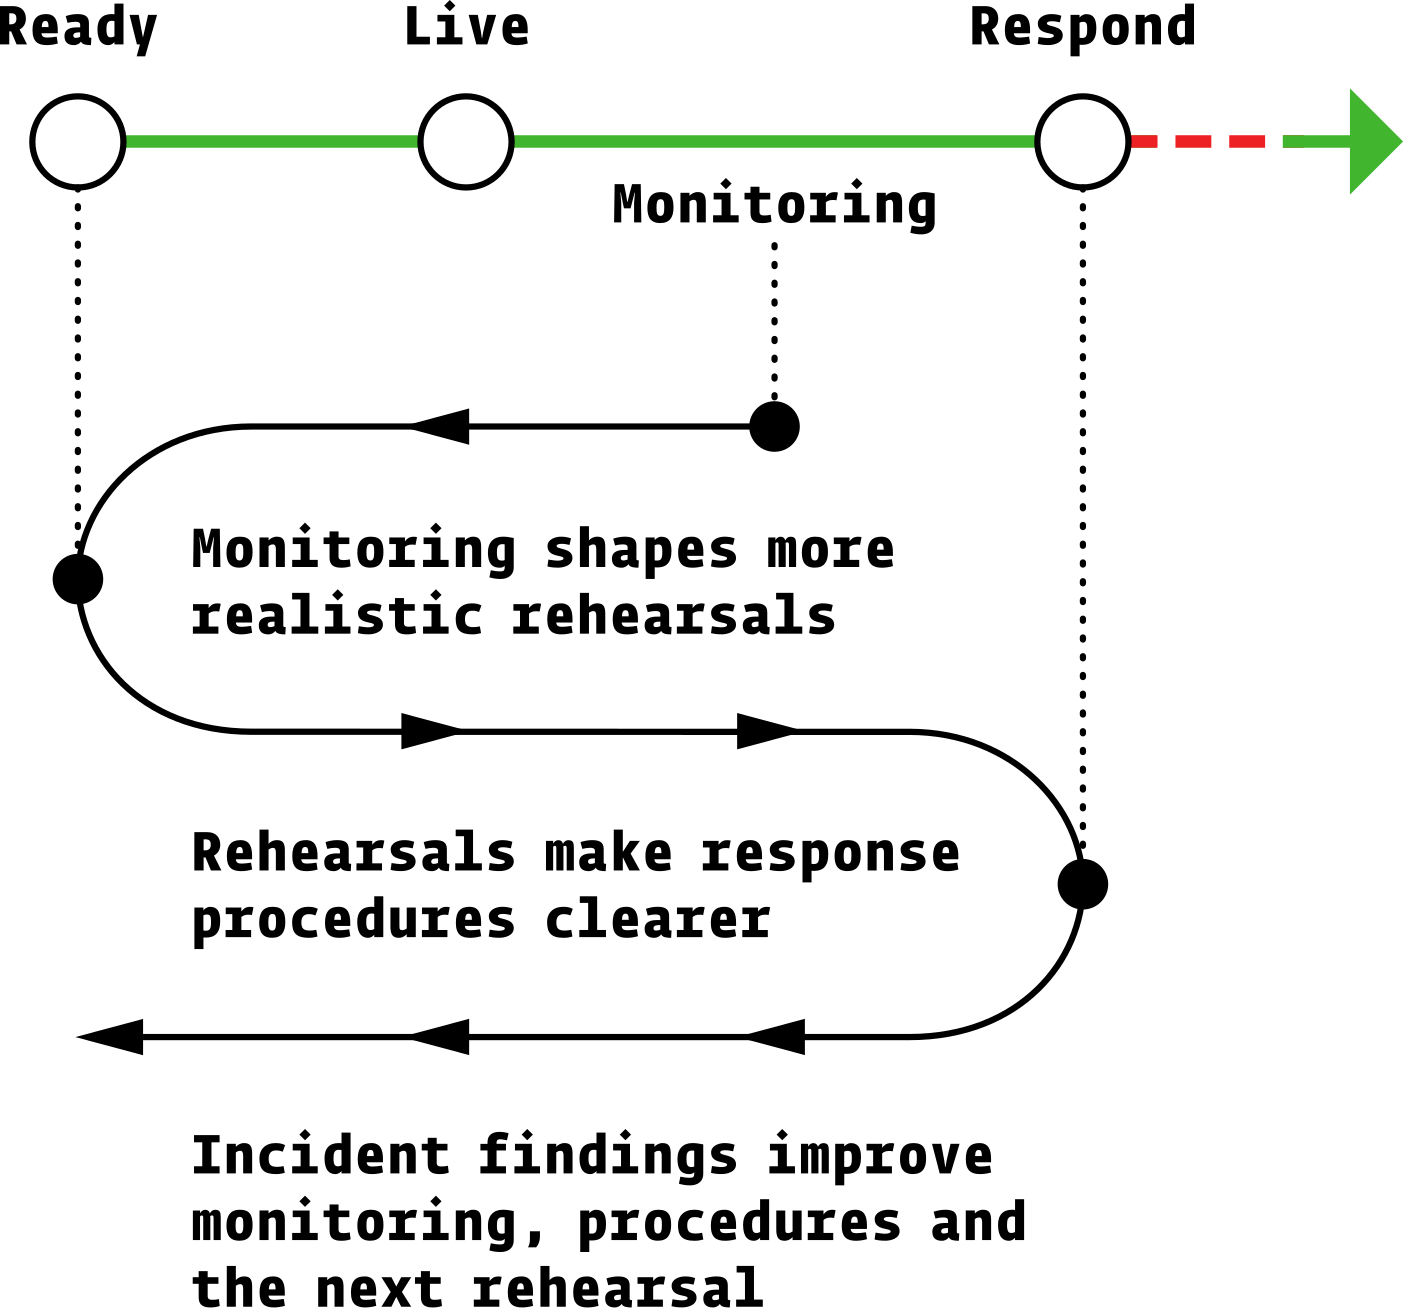
Because each service makes the other two more effective.
- A rehearsal is more valuable when it tests how an incident would actually be detected and escalated.
- An alert is more useful when your team already knows what to do next.
- Response is faster and more informed when the specialists supporting you already understand your environment.
By bringing rehearsal, monitoring and response together, lessons from each part can improve the others. Monitoring helps shape more realistic rehearsals, rehearsals make response procedures clearer, and incident findings help improve future monitoring and preparation.
Ready: what a response rehearsal involves
A realistic cyber incident scenario based on your operation, involving the people who would respond if it happened.
The scenario is built around your site architecture, operating procedures and cause-and effect information rather than a generic template.
| Format | Coverage | Duration |
|---|---|---|
| Desktop rehearsal | Guided discussion testing decisions, responsibilities and escalation. No operational systems are touched. | 2–3 hrs |
| Functional drill | Tests detection, reporting, escalation and response communication. | Half–full day |
| Full-scale exercise | May include vendors, regulatory notification and return-to-service decisions. | Multiple days |
The rehearsal brings together the people who would be involved in a real incident. This may include operations, engineering, IT, health and safety, business leaders and relevant equipment vendors. SIS+ includes one response rehearsal per year as standard.
Additional rehearsals can be added based on the customer’s operational risk, requirements and agreed scope.
What the after-action report contains
A clear record of the exercise, the decisions made, the gaps identified and the actions required, written so it can be used by operational leaders, boards and regulators without being rewritten.
- Timeline of key decisions, including what worked and where escalation was delayed
- Good practices to retain
- Identified gaps and their potential operational consequence
- Clear actions, owners and risk-based priorities
- Evidence suitable for leadership, board and regulatory discussions
- Findings fed back into monitoring, procedures and future rehearsals
Live: why OT needs specialist monitoring
Because activity that looks normal on a corporate network can mean something very different in an OT environment.
In an OT environment, the activity that matters does not always look malicious. It may appear to be normal engineering or maintenance work, but the timing, location or lack of approval can change its significance.
Examples include an engineering workstation connecting to a different network segment, controller logic changing outside the approved process or a vendor remote-access connection remaining active outside the maintenance window. SIS+ Live monitors for these unexpected changes and flags them for investigation.
Context is critical. An internet connection from an office laptop may be expected. The same connection from an engineering workstation on the control network may require immediate attention.
Impact on operations
SIS+ Live monitors OT network activity passively. It is outside the control path and does not send commands or write to controllers or other operational equipment.
If a monitoring component fails, it may affect monitoring capability, but it will not affect the operation itself. During response, the customer retains operational and restart authority.
Respond: the first hours of an incident
An on-call OT cyber specialist helps you assess the incident, consider safe containment options and begin recovery planning while the investigation continues.
| Stage | Typical activity |
|---|---|
| Initial response | Incident reported, specialist engaged, initial information gathered and containment options considered with the operational team. |
| First four hours | Available technical evidence identified, preserved and reviewed. Affected systems and operations assessed. |
| Four to 24 hours | Investigation, containment and recovery options refined. SIS supplies technical information and evidence for leadership and regulatory communications. |
| Beyond 24 hours | Recovery support continues. Where included, baseline comparison supports return-to-service decisions. Customer retains restart authority. |
| After the incident | Every activation includes a post-incident report. Findings improve monitoring, procedures and rehearsals. |
SIS+ Respond availability and response times are agreed with each customer during scoping and recorded in the service agreement. Customer approves communications.
The customer may submit them directly, or SIS can prepare and submit notifications on the customer’s behalf where agreed.
What SIS+ looks like in practice
Three situations you may recognise, and how SIS+ helps you prepare, monitor and respond.
1.Vendor access left open
A vendor is given remote access during a maintenance window, but the connection remains open afterwards.
| Live | Identifies when a remote-access connection is active, when it remains open outside an approved maintenance window, and activity taking place through that connection. |
|---|---|
| Ready | The procedure identifies who can close access outside business hours and who has authority. |
| Respond | May not need activation. The event can improve future rehearsals and procedures. |
2. Controller logic changed without approval
A change is made to controller logic outside the approved change process.
| Live | Detects controller-logic changes. Where baseline comparison is included, it compares current logic against the approved version and identifies differences. |
|---|---|
| Ready | The procedure identifies who verifies the change and authorises rollback. |
| Respond | Can be activated if the change cannot be verified and further investigation or recovery support is required. |
3. Ransomware on the corporate network
Ransomware affects the corporate network, and it is not yet clear whether OT systems can be reached.
| Live | Shows which OT assets may be reachable and which connections remain active. |
|---|---|
| Ready | The team follows rehearsed escalation and containment with clear operational authority. |
| Respond | OT cyber specialists help investigate and contain the incident while recovery planning begins. |
Who SIS+ is for
SIS+ is designed for owners and operators of renewable energy assets, including wind, solar and battery storage. The service also supports OT environments across electricity networks, water utilities, oil and gas, transport, mining and other critical infrastructure sectors.
SIS+ is delivered across Australia and the Middle East. Its reporting and service evidence can support customer obligations under applicable legislation and recognised cyber security frameworks, including Australia’s SOCI Act and the Australian Energy Sector Cyber Security Framework where relevant.
How SIS+ starts
We confirm the scope, understand your current environment and then activate monitoring, response support and the first rehearsal.
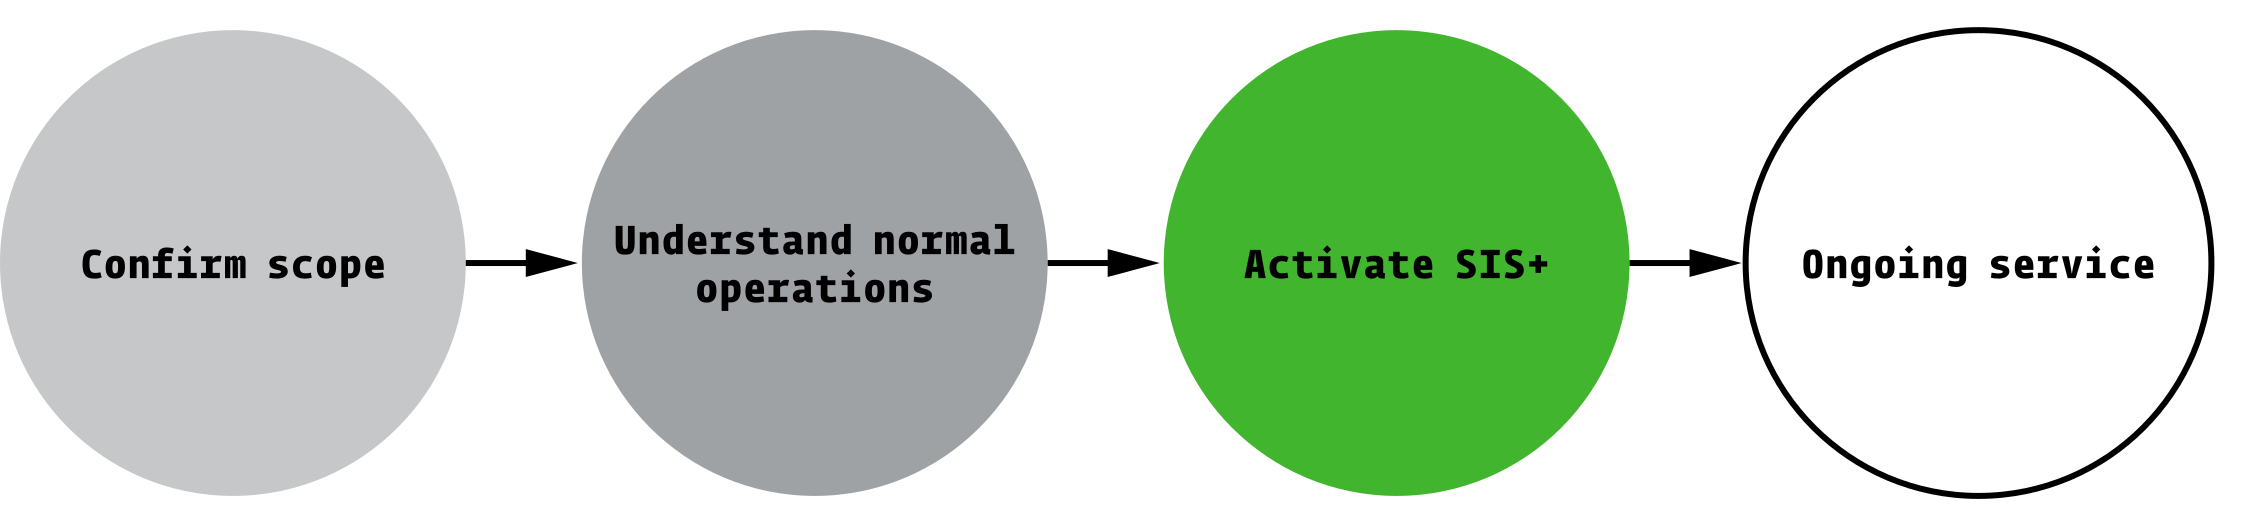
Confirm scope
Review sites, environment, controls, concerns and response support.
Understand normal operations
Map relevant connections and establish a baseline.
Activate SIS+
Monitoring and response support begin; first rehearsal scheduled.
Ongoing service
Monthly reporting and review, plus rehearsals at the agreed frequency.
The onboarding schedule is agreed with each customer during scoping.
The business benefits of SIS+
SIS+ helps owners and operators reduce operational cyber risk, improve incident readiness, and provide assurance to leadership, boards and regulators.
- Greater visibility of operational cyber risk
- Faster, more coordinated incident response
- Reduced likelihood and impact of operational disruption
- Safer containment and recovery decisions
- Greater assurance for executives, boards and regulators
- Continuous improvement through monitoring, rehearsals and incident lessons
Supporting service outputs include monthly reports, service reviews, response rehearsals, after-action reports and post-incident reviews.
What SIS+ costs
SIS+ is priced per site, per month. The fee reflects the number of sites, the size of the monitored environment and the level of response support required.
The service term is agreed with each customer during scoping and recorded in the service agreement.
Common questions
We already have an asset register. What does monitoring add?
Your asset register shows what is installed. SIS+ Live shows what is communicating, what may be reachable and what has changed outside approved operating conditions.
SIS+ Live complements the asset register by monitoring network communications and changing exposure. It does not replace the register or the processes used to maintain it.
Where is monitoring data stored, and who can access it?
Monitoring-data hosting is agreed with each customer and recorded in the customer’s service agreement. Data can be hosted in Australia, the UAE or another location selected by the customer.
Access is limited to SIS specialists assigned to the customer. Provider access depends on the selected hosting arrangement and is documented in the service agreement.
Data is used only to deliver and support that customer’s SIS+ service. It is only shared where required by the agreed service arrangements and with customer approval and consent.
Customers can access and export their data. Retention is agreed with each customer. When the service ends, data can be returned or exported, retained for an agreed period, or securely deleted. SIS may retain data where required by law or contract.
What does SIS+ Respond not do?
SIS+ Respond supports your team with specialist advice and evidence. It does not take control of your operation or make operational decisions for you.
- Does not replace emergency response arrangements, safety systems or safety instrumented functions
- Does not control plant or operational systems
- Does not authorise shutdown or restart
- Does not conduct legal or insurance investigations, but can provide technical information and evidence
How does SIS+ fit with the operational practices already in place?
SIS+ builds on the operational, safety and risk-management practices you already use.
| Practice | How SIS+ supports it |
|---|---|
| Management of change | Identifies unexpected controller, configuration or network activity. |
| HAZOP and LOPA | Provides cyber information for existing hazard and risk assessments. |
| Alarm management | Cyber alerts remain separate from process alarms and use agreed escalation. |
| Emergency response | Adds cyber scenarios, responsibilities and escalation. |
| Return to service | Where baseline comparison is included, SIS can compare current controller logic against the approved version and provide findings to support the customer's return-to-service decision. |
What makes SIS independent?
SIS+ is service-led, with recommendations based on what best fits your operation.
Where a product or platform is required, SIS assesses available options and recommends a suitable fit. The technology decision remains yours.
How does SIS+ relate to the SIS OT Cyber Pulse?
The SIS OT Cyber Pulse shows where you stand at a point in time. SIS+ helps you maintain and improve your OT cyber security over time.
A Pulse assessment is not required before starting SIS+. Existing findings can help define scope and reduce unnecessary discovery work.
Who delivers SIS+
SIS+ brings together OT cyber security capabilities that SIS has delivered for more than 15 years, providing them through one ongoing managed service.
Our OT cyber security experience:
- More than 15 years specialising in OT cyber security
- More than 300 industrial and OT environments assessed
- ISO 9001, ISO 27001, ISO 42001 accredited
- Australian Cyber Consultant of the Year (SME), 2026
The team
SIS+ is delivered by OT cyber specialists familiar with your environment, service scope and response arrangements.
Depending on the customer’s needs, SIS+ may be delivered by one core team or by separate specialist teams that share customer knowledge across response rehearsals, monitoring and incident response.
Ready to
discuss SIS+?
Want to see what a response rehearsal produces?
Not sure where to start?